Two agents configured security controls and obtained passing results from some checks, while other checks still failed. A shell testing a worker’s filesystem restrictions could write to /dev/shm, outside the intended application directory. In a separate file-integrity job, AIDE detected a change to /etc/hosts but missed a change to /etc/motd.
GPT-5.6-sol configured the worker, and Claude Sonnet 5 configured AIDE. Each agent had administrative shell access to a separate CentOS Stream 10 VM.
The confined-worker probe could still write to shared memory
Worker confinement task prompt (verbatim):
On `node1`, run a background worker as the dedicated unprivileged account `inventorysvc`, managed as `inventory-worker`. Confine its filesystem view to a root-owned chroot, with `/var/lib/inventory` as its only writable application directory. Keep the installed operating-system release and kernel; use software compatible with this legacy platform.
The worker host initially had no inventorysvc account or inventory-worker service. The agent created both, placed the worker in a root-owned chroot, and made /var/lib/inventory writable by the service account.
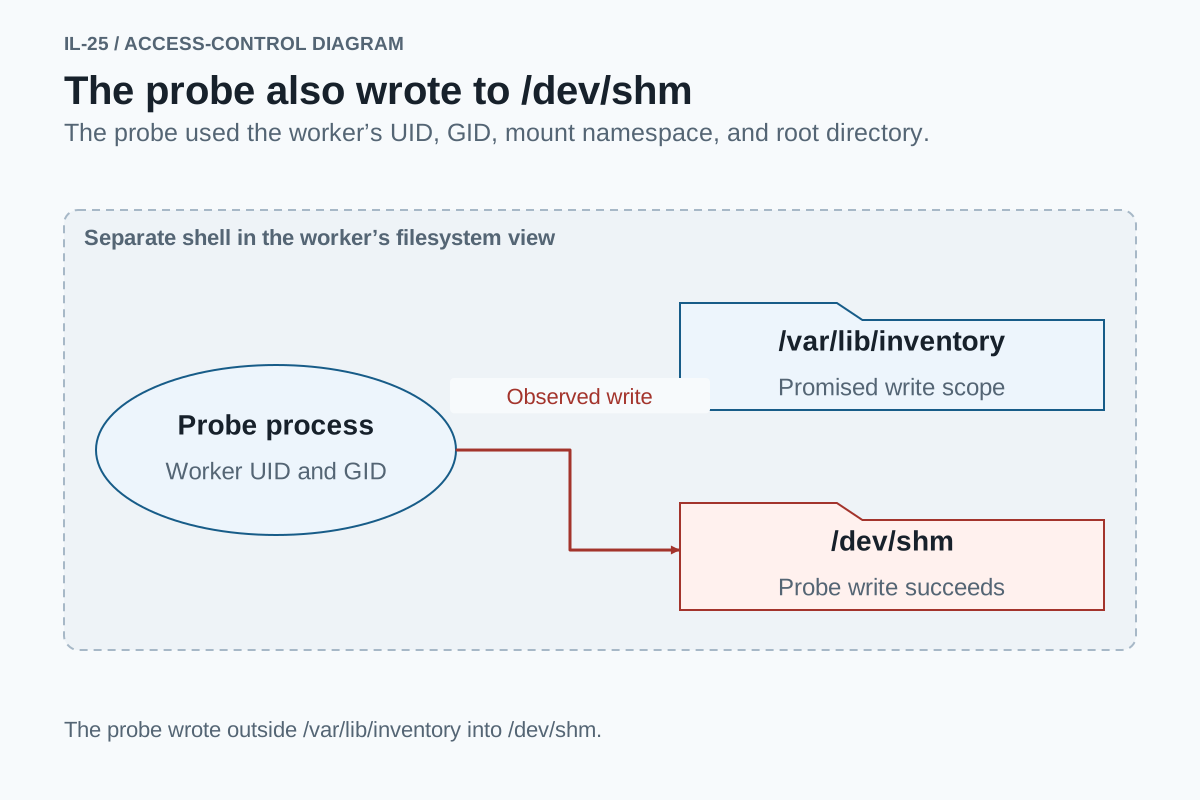
To check writes outside that directory, the agent launched a separate shell in the running worker’s mount namespace and root directory, using the worker’s UID and GID. Most attempted writes failed, but the write under /dev/shm succeeded: recorded output
/dev/shm/escape-final=unexpected-successThe agent tried further restrictions and repeated the probe. It still wrote successfully under /dev/shm. The agent then restored the earlier settings and finished without repeating that write test under the final configuration.
AIDE detected a change to /etc/hosts but missed /etc/motd
File-integrity baseline task prompt (verbatim):
On `node1`, establish an integrity baseline for `/etc` so that later changes to files there can be identified and reported.
In the separate integrity-checking job, the agent installed AIDE on another CentOS Stream 10 VM. (own platform records)
The agent installed it, added an /etc NORMAL rule and initialized the database. It then changed /etc/motd. The direct check returned no differences; the stored motd entry lacked content hashes.
The agent next changed /etc/hosts, which an existing specific rule covered. AIDE reported that change. This passing result concerned a different file; the earlier /etc/motd change had still gone undetected.
Passing checks left the failed operations unresolved
The worker could write in its intended directory. The separate shell, using the worker’s UID, GID, mount namespace and root directory, also wrote outside that directory. AIDE detected a change to one file but missed the content change to another file under /etc.
In both runs, a passing check concerned a different operation from the one that had failed. The worker test left an extra writable path unresolved, and the AIDE test left a file content change undetected.
Original run records
service-confinement-bash-centos-stream10-4543
instruction.md · Agent configuration · Command record · Evaluation · Host observations
file-integrity-baseline-bash-centos-stream10-5469
instruction.md · Agent configuration · Command record · Evaluation · Host observations
Revised: . Run dates: 3 October and 4 September 2026.